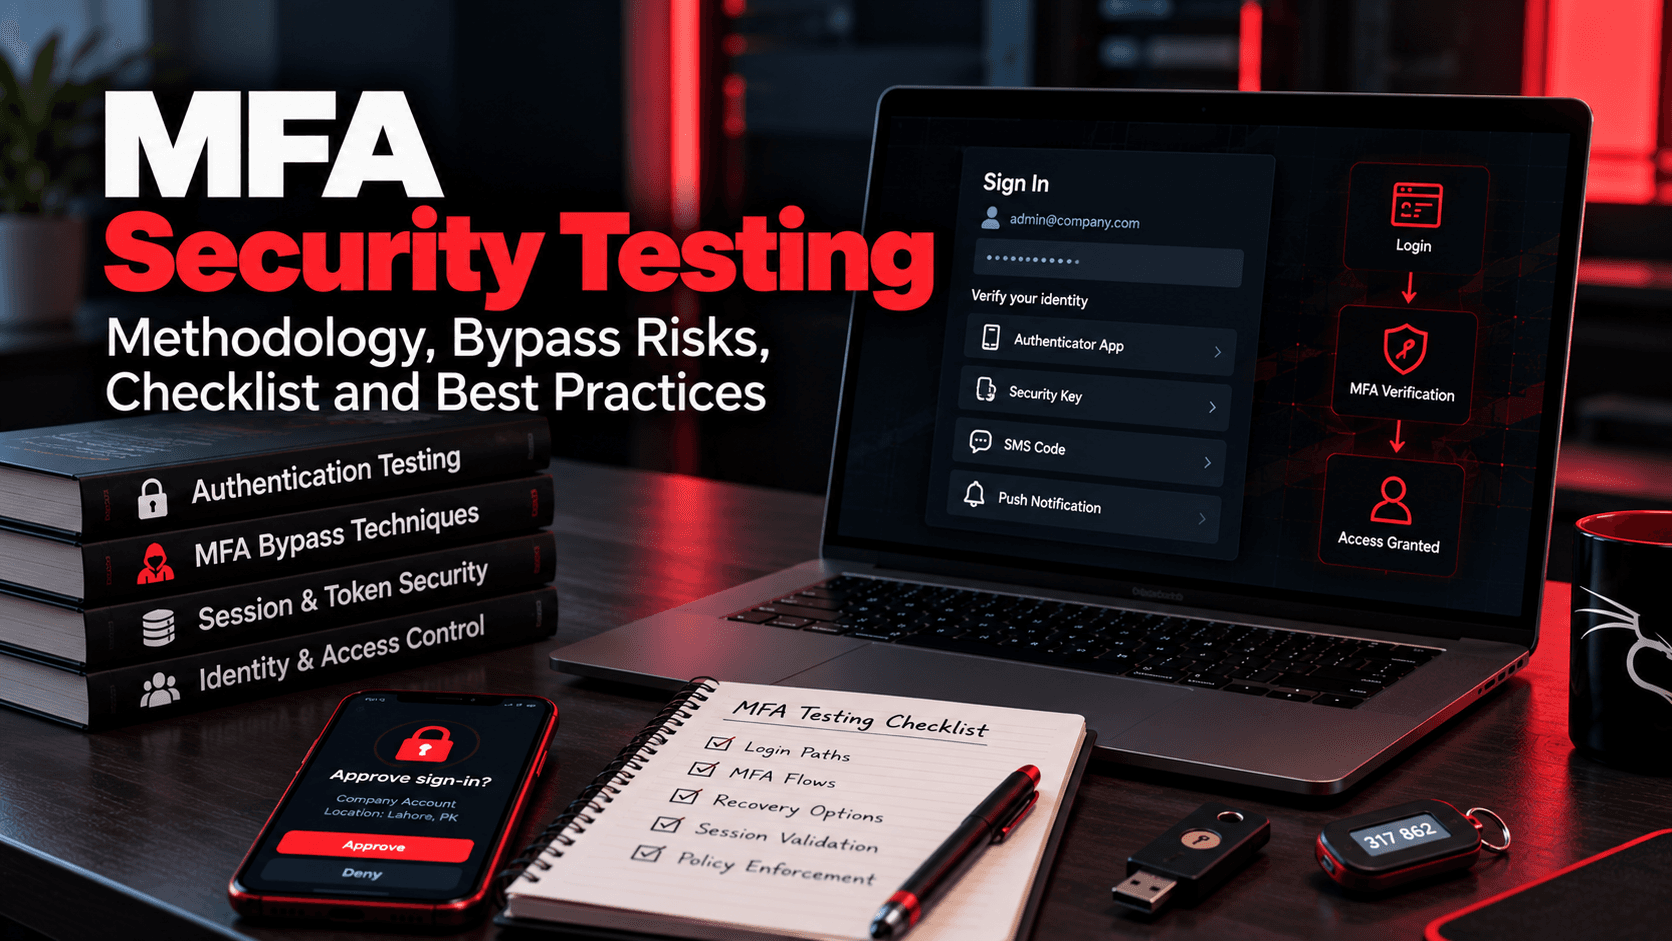
MFA security testing checks whether an attacker with a valid password can still get into an account. It covers login paths, recovery methods, policy exceptions, and session tokens, not just whether MFA is switched on. MFA usually fails in the gaps around the factor, not in the factor itself, which is the same reason MFA alone doesn't stop account takeovers.
What is MFA security testing?
An authorized test that checks whether attackers can bypass or weaken your multi-factor authentication.
How do you test multi-factor authentication?
With written permission, map every login path, then test factors, MFA enforcement, recovery, and session handling.
Can MFA be bypassed during a penetration test?
Yes, when implementation gaps exist, such as endpoints that skip MFA, reusable codes, or weak recovery.
What are the most common MFA security weaknesses?
Unprotected APIs, legacy authentication, broad policy exclusions, weak recovery, MFA fatigue, and sessions that last too long.
How often should MFA security testing be performed?
There's no fixed rule. Test after major authentication changes and as part of regular penetration testing.
Key Takeaways
- Attackers target the paths, fallbacks, and sessions around MFA, not the factor itself.
- A configuration review shows MFA is on; a test shows whether it holds.
- Security keys and passkeys with user verification resist credential phishing, but they don't protect a stolen session.
- Recovery processes and the help desk need the same scrutiny as the login page.
- Manual testing finds the logic and process gaps automated checks miss.
What Is MFA Security Testing?
MFA security testing covers the whole authentication journey around the second factor. It follows guidance such as NIST SP 800-63B-4 and needs written authorization, an agreed scope, and compliance with applicable laws, contracts, and your identity provider's terms. A typical scope covers five areas:
- Factors: SMS, authenticator apps, push, security keys, and passkeys.
- Login paths: web, mobile apps, APIs, VPN, single sign-on, and legacy protocols.
- Enforcement: the policies that decide when MFA is required.
- Recovery: backup codes, factor resets, new device enrollment, and help desk processes.
- Sessions: the cookies and tokens issued after login.
Why MFA Implementation Still Needs Security Testing
MFA is one of the most effective controls available. In one case, a company found stolen admin credentials on the dark web and accelerated its MFA rollout in response, and the lessons noted that VPNs, internal access controls, and MFA make stolen credentials far less useful.
Less useful isn't useless. A login API that skips MFA, an old policy exclusion, or an easy factor reset all give an attacker a way around it. Microsoft made this point in its 2022 report on a large adversary-in-the-middle phishing campaign: this is not a vulnerability in MFA. The attackers took the session after the user had completed MFA, the same technique behind kits like Mirage2FA.
Must Read: Mirage2FA: The Microsoft 365 Phishing Kit That Bypasses Conventional MFA
MFA Security Testing Methodology
MFA testing follows the same phases as any engagement, which we cover in our guide to penetration testing methodology. Before testing, you agree the scope, test accounts, and limits, such as no testing against real employees' devices without separate approval.
1. Authentication Factors and MFA Flows to Test
Start by mapping every login path, the factors allowed on each, and the order the checks run in. Each factor resists some attacks and not others:
- SMS and voice codes: better than a password alone, but exposed to SIM swapping, number porting, and phishing. NIST SP 800-63B-4 treats the phone network as a restricted authenticator.
- Authenticator app codes (TOTP): resist SIM swapping, but a user can still type a code into a phishing page.
- Push approvals: simple approve-or-deny prompts are open to MFA fatigue. Number matching helps but isn't phishing-resistant.
- Security keys and passkeys (FIDO2/WebAuthn): use cryptographic authentication tied to the real website, which resists credential phishing. Passkeys with user verification, such as a PIN or biometric, provide MFA; without it, they're single-factor. Stolen sessions and weak recovery can still undermine them.
NIST SP 800-63B-4 states that OTP and out-of-band methods aren't phishing-resistant, and requires verifiers to offer at least one phishing-resistant option at AAL2. The tester checks which methods each path actually accepts. Where even strong factors fall short is covered in our post on passkey security and bypassing phishing-resistant MFA.
2. Common MFA Bypass Techniques
Here the tester looks for a signed-in state without a real second factor:
- Flow and logic flaws: a pre-MFA session or token that reaches protected resources, or a client-side value that tells the server MFA was passed.
- Unprotected paths: an API, mobile endpoint, legacy protocol, or alternate sign-in page that accepts a password without MFA.
- Weak code handling: one-time codes that can be reused, stay valid too long, or have no attempt limit.
- Downgrade and fallback: a user enrolled in a security key can still choose "text me a code," and so can an attacker.
- Adversary-in-the-middle phishing: a proxy relays the real login, MFA step included, and captures the session cookie. Microsoft reported one campaign that targeted more than 10,000 organizations since September 2021. Phishing-resistant methods such as FIDO2 are the main defense.
The OWASP Web Security Testing Guide's MFA cases cover these. Not every technique applies everywhere, so the tester shows which are realistic for your setup.
3. Conditional Access and MFA Enforcement Testing
Identity provider policies decide when MFA applies, based on user, application, location, device, and risk. The tester looks for the exceptions: excluded users, groups, service accounts, and apps; trusted IP ranges that skip MFA; legacy authentication that can't enforce it; device compliance checks an unmanaged laptop can pass; and policies left in report-only mode. Emergency access accounts should be excluded deliberately and monitored closely.
4. MFA Recovery and Fallback Security Testing
Recovery lets people in when their factor is missing, so attackers look there early. The tester checks backup codes, self-service resets, new device enrollment, and changes to recovery contact details, and the help desk too. The joint FBI and CISA advisory on Scattered Spider, updated in July 2025, describes threat actors posing as employees to get help desk staff to reset passwords and move MFA to devices they control.
Helpful for you: Social Engineering and Phishing Simulation
5. MFA Fatigue, OTP, and Push Notification Testing
For push, the tester checks whether prompts show enough context, whether number matching is enforced, whether repeated prompts are rate-limited, and whether repeated denials raise an alert. NIST SP 800-63B-4 requires out-of-band approvals to be linked to the specific login through an authentication secret; simple approve-or-deny prompts without this are vulnerable to fatigue attacks. Uber's 2022 breach shows why: an attacker with a contractor's stolen password triggered repeated approval requests until the contractor accepted one, and the attacker logged in. For one-time codes, the tester checks expiry, single use, session binding, and attempt limits. NIST caps consecutive failed attempts at no more than 100, and many apps set lower limits. Fatigue testing against real staff happens only when explicitly in scope.
Session and Token Security Testing
MFA protects sign-in. After that, the session cookie or token is the account, and if adversary-in-the-middle phishing or infostealer malware steals it, the attacker may not need MFA at all. Our guide to session hijacking: types, risks, and prevention explains how this happens. The tester checks:
- Lifetime: how long sessions and refresh tokens last.
- Revocation: whether sessions end after a password change, MFA reset, or sign-out.
- Binding: whether a stolen token works from another device, and whether token protection is used where available.
- Cookie settings: Secure, HttpOnly, and SameSite flags, and whether the session ID changes after login.
- Step-up: whether changing MFA or recovery settings requires signing in again.
- Non-interactive access: OAuth grants, API keys, and app passwords that give long-lived access without MFA.
APIs need the same checks, which is why API security testing covers token handling and OAuth flows directly.
Manual vs Automated MFA Security Testing
Automated tools check settings at scale. Manual testing finds the logic and process gaps around MFA.
Aspect | Automated testing | Manual testing |
|---|---|---|
What it does best | Checks policies and configs across many users and apps quickly | Tests how flows, recovery, and sessions behave in practice |
Coverage | Broad and repeatable | Deep on the paths that matter most |
Typical findings | Users without MFA, legacy authentication enabled, policy exclusions, weak allowed methods | MFA step skipped through an alternate path, reusable codes, weak recovery, tokens that survive revocation |
Business logic | Limited | Strong |
Help desk and process review | Not covered | Covered when explicitly in scope |
Chaining issues into an attack path | Generally not | Yes, shows how gaps connect |
Best used for | Continuous monitoring between tests | Launches, major changes, and regular assessments |
Also Read: DAST vs Penetration Testing
MFA Security Testing Checklist
- Confirm written authorization, scope, test accounts, and rules of engagement.
- Map every login path: web, mobile, APIs, VPN, remote access, SSO, and legacy protocols.
- List the MFA methods allowed on each path and confirm which are phishing-resistant.
- Check that the MFA step can't be skipped by changing requests, responses, or the order of steps.
- Confirm no pre-MFA session or token can reach protected resources before MFA completes.
- Test OTP expiry, single use, session binding, and failed-attempt limits.
- Test push prompts for context, number matching, rate limits, and alerts on repeated denials.
- Check whether users can fall back from a strong method to a weaker one.
- Review conditional access exclusions, trusted locations, report-only policies, and emergency access accounts.
- Test backup codes, self-service resets, new device enrollment, and recovery contact changes.
- Review help desk identity verification, with separate approval if social engineering is in scope.
- Test session lifetime, revocation, cookie settings, and re-authentication for MFA or recovery changes.
- Review OAuth grants, app passwords, and API keys that bypass interactive sign-in.
- Confirm failed MFA attempts and suspicious prompts are logged and alerted, then retest after fixes.
MFA Security Testing Best Practices
- Move to phishing-resistant MFA. CISA strongly encourages FIDO2 security keys or passkeys. Start with administrators.
- Use number matching in the interim. CISA calls it one of the best interim mitigations for push fatigue.
- Close every path. Enforce MFA on APIs, mobile apps, and remote access, and turn off legacy authentication.
- Remove weak fallbacks. Don't let users drop from a strong method to SMS without a documented reason.
- Harden recovery. Make factor resets as hard to abuse as the factor itself.
- Keep exclusions small. Give every policy exclusion an owner, a reason, and a review date.
- Shorten and protect sessions. Set lifetimes by sensitivity and revoke sessions after credential or MFA changes.
- Watch MFA activity. Alert on repeated prompts, new MFA registrations, and recovery changes.
- Test after changes. Retest after new apps, identity provider changes, or policy rework.
How OraSec Can Help
OraSec tests MFA as part of web application security testing, where we evaluate login flows, session handling, password resets, and multi-factor authentication. We map every way into your accounts, test each factor, fallback, and policy, and follow sessions after login. Each finding comes with evidence, business impact, and a practical fix. When help desk or user-facing testing is in scope, we agree the approach and limits with you first, and we retest once fixes are in. The team's own research has produced published CVEs (CVE-2025-50847 through CVE-2025-50850).
Conclusion
MFA is still one of the best defenses against account takeover. The risk sits in the gaps around it: a path that skips it, a policy with too many exceptions, a recovery process that's easy to talk past, or a session that outlives the login. MFA security testing finds those gaps before an attacker does. If you want to know whether your MFA holds across every path into your accounts, talk to our team.
Frequently Asked Questions
Is MFA testing part of a standard penetration test?
Web application penetration tests often include MFA when authentication is in scope. A dedicated assessment also covers identity policies, recovery, help desk, and sessions.
Are passkeys immune to MFA bypass?
No. Passkeys strongly resist phishing and relay attacks, but they don't protect a stolen session or a weak fallback or recovery path.
Will MFA testing lock out real users?
It shouldn't. Testers use dedicated accounts, agreed rate limits and windows, and test real users only with explicit approval.
Do you test the IT help desk?
Only when it's in scope and approved in writing, with agreed scenarios, named staff, and a clear way to stop the test.
Can MFA testing be done on Microsoft Entra ID or Okta?
Yes. Testing covers what you configure, such as policies, allowed methods, exclusions, recovery, and session settings, within the provider's testing terms.
What should we prepare before an MFA security test?
Test accounts for each MFA method you support, a list of applications and login paths, and an export of your MFA and conditional access policies.