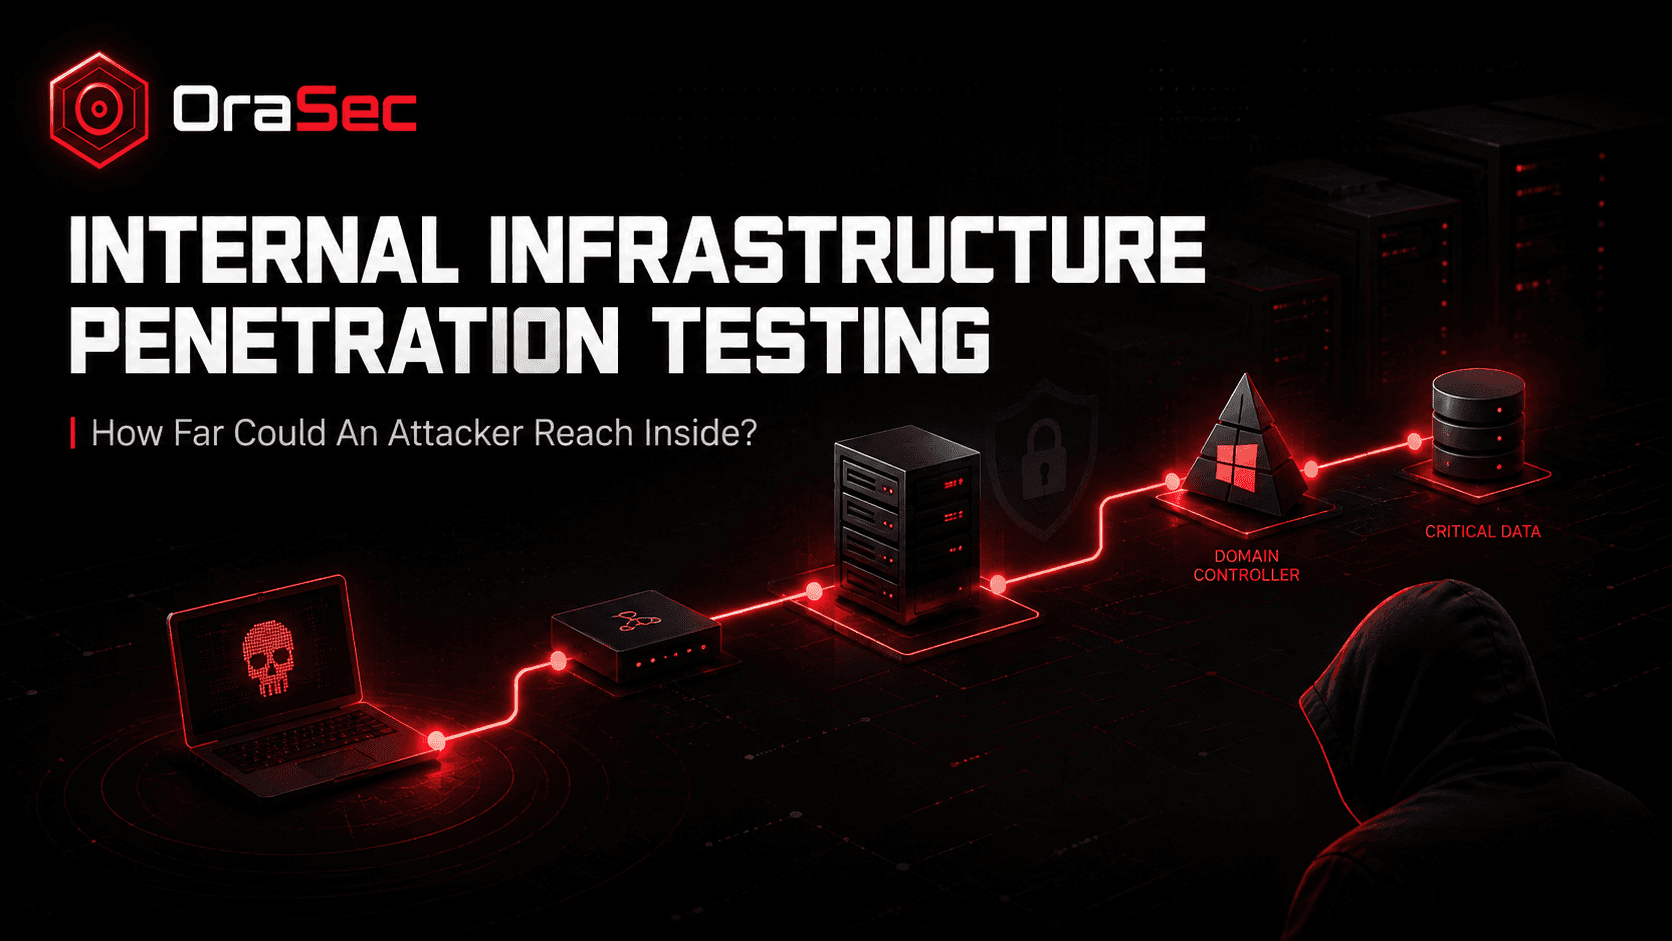
External testing focuses on what an attacker can reach from outside. Internal testing asks what happens after an attacker gains a foothold inside the network.
What Is Internal Infrastructure Penetration Testing?
Internal infrastructure penetration testing tests security from inside the network. The tester usually starts from an assumed-compromise position, such as internal network access, a standard user account, or a compromised workstation, depending on the agreed scenario.
From there they test what external assessments rarely touch: Active Directory, file and database servers, workstations, segmentation, and the trust relationships between them.
The focus is not the external perimeter. It is what an attacker can reach and escalate to after gaining internal access.
Why Does It Matter?
Many organisations focus heavily on external exposure while giving less attention to internal attack paths.
Internal networks are often flatter than intended, with broader access rights and lighter monitoring. Internal testing measures that gap first.
How Does the Testing Process Work?
1. Scoping. Define boundaries, critical assets, and rules of engagement. Agree whether testing is black box, grey box, or white box.
2. Reconnaissance. List servers, workstations, and network devices. Map user roles, domain structure, and segmentation.
3. Threat modelling. Identify high-value targets such as Active Directory, file servers, and databases, then map likely routes to each.
4. Exploitation and privilege escalation. Exploit weaknesses to gain access, then try to escalate through weak settings, weak passwords, or unpatched software.
5. Lateral movement and persistence. Where authorised, test movement between systems using captured credentials and assess whether endpoint controls detect it. Persistence techniques should only be used when permitted by the rules of engagement.
6. Impact analysis. Establish what sensitive data is reachable and, where authorised, test whether monitoring or DLP controls detect simulated exfiltration.
7. Reporting and retesting. Document findings with severity, evidence, and repro steps, then verify fixes rather than assuming they held.
What Does Internal Testing Usually Find?
- Weak password policies, reused credentials, and insecure authentication controls
- Unpatched internal systems and applications
- Excessive user rights and standing admin access
- Flat networks with too little segmentation
- Misconfigured internal services and cloud connections
- Service accounts with more access than they need
Common Mistakes
- Testing externally only. The perimeter is one control; internal exposure decides the impact.
- Scoping around convenience. Scoping only the easiest systems can hide important attack paths. Critical or production systems should be included where safe and appropriate, or covered through agreed alternatives when direct testing is too risky.
- Taking a findings list without attack paths. Single issues matter less than the chain they enable.
- Skipping the retest. A fix nobody checked is an assumption.
- Testing yearly regardless of change. Systems shift, so test timing should follow.
What Tools Do Testers Use?
A good internal test combines automated tooling with manual work. Common tools:
- Nmap for host and service discovery
- BloodHound for mapping Active Directory attack paths and privilege relationships
- Metasploit for exploitation and post-exploitation
- Wireshark for traffic analysis
- Responder for testing name-resolution poisoning exposure
- Burp Suite for internal web apps and APIs
Tools identify potential weaknesses. Manual analysis is still important for understanding which findings can be chained into meaningful attack paths.
What Should You Expect From a Provider?
Ask before the engagement, not after the report:
- Relevant qualifications such as OSCP, GPEN, CREST Registered Penetration Tester (CRT), or CREST Certified Tester – Infrastructure (CCT INF), along with suitable infrastructure-testing experience
- A documented method that follows a known standard
- Reports that include attack paths and repro steps, not just severity labels
- Retesting of fixed findings, and whether it is included or charged extra
- A debrief for both technical and business stakeholders
How OraSec Can Help
OraSec tests what happens after an attacker gets in. We map internal attack paths, measure what one compromised account reaches, and check whether your monitoring raises an alert anyone acts on. Findings come with repro steps and a retest, not a scanner export.
Conclusion
Internal infrastructure penetration testing answers what a compliance scan cannot: what does an attacker actually reach from inside your network?
Scope it properly, ask for attack paths rather than lists, and verify the fixes held. The value is not the report. It is what you know afterwards.
FAQs
How often should we run internal testing? Use a risk-based schedule and retest after significant infrastructure, identity, or access-control changes. Some compliance frameworks may also require annual testing.
How is this different from vulnerability scanning? Scanning identifies potential weaknesses. Internal penetration testing attempts to validate and safely chain them, where permitted, to show what an attacker could actually achieve.
Do we need internal testing if we already test externally? They answer different questions, so most organisations need both.
Will testing disrupt production systems? Scope and rules of engagement are agreed in advance, including excluded systems and restricted techniques. Disruption risk should be discussed before testing begins.
What should the report include? Severity ratings, evidence, repro steps, the attack paths involved, and prioritised fix guidance a team can act on.